
A guide to AI application testing strategy
High level, an AI testing strategy is just a structured approach to...
Learn how to build an effective API testing strategy with best practices, testing approaches, automation tips, and CI/CD integration guidance.
TL;DR
Testing is such a fundamental part of software engineering that every developer, be it a fresh college graduate or an experienced individual contributor, talks about it every day until they retire. Testing is much more than validating the accuracy of the product.
It is a strategic enabler that dictates how fast a team can ship, how confidently they can refactor, and how quickly they can recover from failure.
In this guide, we will explore the blueprints for building a testing strategy that accelerates development rather than slowing it down.
An API testing strategy is a comprehensive plan that defines how your team will validate the functionality, performance, and security of your application programming interfaces.
It dictates not just what tools you will use, but when tests are executed, who is responsible for them, and how they align with your broader business objectives.
A robust API testing strategy reduces time to market by catching integration errors early in the software development life cycle.
A strategy elevates you from simply “writing automated tests” to actually governing quality.
It helps you be ready with the answers for queries such as “How do we handle authentication in our test environments?” “What is our approach to mocking third-party endpoints?” And “How do we ensure our tests don’t pollute the database?”
By standardizing these complex, repetitive tasks, a solid strategy removes the guesswork. Instead of reinventing the wheel for every new release, your team operates from a clear, scalable blueprint that ensures total visibility across your architecture.
A robust API testing strategy reduces time to market by catching integration errors early in the software development life cycle.
“APIs are forever.”
Amazon CTO Werner Vogels has often highlighted this painful truth. Once you publish an API and other teams (or external customers) start consuming it, changing that contract without breaking downstream systems becomes incredibly difficult.
Without a cohesive plan, teams usually fall into the trap of over-relying on UI testing. They spin up Selenium or Playwright, click everything on the front end, and assume that the underlying APIs are fine. But UI tests are notoriously brittle, slow, and expensive to maintain.
By the time a UI test catches an API error, you’re probably far along in the release cycle, making the bug significantly more expensive to fix.
You wouldn’t use a sledgehammer to hang a picture frame, and you shouldn’t use a massive, resource-heavy load testing suite to verify a simple internal CRUD operation. A mature strategy categorizes tests by their specific purpose and executes them at the appropriate time.
This is the bread and butter of API testing. Functional testing helps you know if the API does exactly what the business logic dictates it should do.
Functional testing goes beyond simply checking for a 200 OK status. It involves validating the response payload against the database state.
If I send a valid POST request to /api/v1/users, I expect a 201 Created status with a response body containing the new user’s ID, and I expect to be able to query the database and find that user.
APIs rarely exist in a vacuum. Integration testing verifies that your API communicates correctly with databases, internal microservices, and external third-party APIs.
If your order-processing API needs to talk to a fulfillment microservice and a third-party shipping API, integration testing ensures the entire chain holds together.
This is arguably the most underutilized but highly effective form of API testing. Contract testing ensures that the producer and consumer of an API agree on the format of the requests and responses.
If the backend team decides to change a response field from userID to id, contract tests fail immediately, preventing the frontend application from crashing in production because it was looking for a key that no longer exists.
Contract testing ensures that the producer and consumer of an API agree on the format of the requests and responses.
Security testing goes far beyond checking for an SSL certificate.
It involves fuzzing, injecting malicious payloads (like SQL injection or cross-site scripting via JSON values), testing authorization bypasses (can a standard user access a /admin endpoint?), and ensuring sensitive data isn’t exposed in error messages.
API security testing validates that endpoints properly authenticate requests, authorize actions, and reject malformed or malicious inputs.
What happens when 10,000 users hit your endpoint simultaneously? Performance testing measures response times and identifies bottlenecks under stress. It tells you whether your API can handle Black Friday traffic or if it will buckle under the weight of connection timeouts and database locks.
It is incredibly common for teams to conflate a “strategy” with “automation.” Let’s clear that up right now.
Buying a set of expensive chef’s knives doesn’t mean you have a strategy for running a commercial kitchen; it just means you can cut things faster. Similarly, writing automated scripts isn’t a testing strategy.
| Feature | API testing strategy | API test automation |
| Focus | The “Why,” “What,” and “When” | The “How” |
| Scope | Team alignment, coverage goals, risk prioritization, CI/CD stages | Script execution, assertions, data generation, pipeline triggers |
| Output | A documented framework guiding engineering decisions | Code, scripts, or configuration files that execute test steps |
| Primary challenge | Aligning stakeholders, securing budget, and managing test data environments | Flaky tests, maintaining scripts, parsing complex JSON/XML responses |
Your strategy dictates what you should automate. Automation is simply the vehicle that executes the strategy.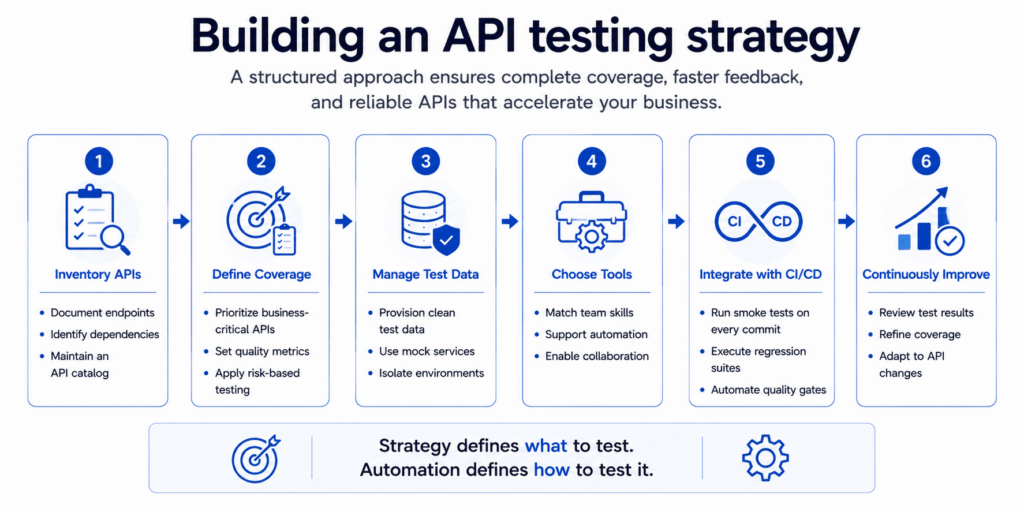
Creating a strategy from scratch can feel like boiling the ocean. I used to make the mistake of trying to overplan and map out every single use case on day one, which usually resulted in a massive, unreadable spreadsheet that was outdated by day three.
Instead, it is of utmost importance to build your approach systematically.
If you don’t have a centralized API catalog, you don’t have a strategy. Instead, you have a guessing game.
You can’t test what you don’t know exists. Therefore, start by documenting your endpoints. Use OpenAPI (Swagger) specifications to establish a single source of truth.
Identify which APIs are public-facing, which are strictly internal, and which rely on third-party dependencies. If you don’t have a centralized API catalog, you don’t have a strategy. Instead, you have a guessing game.
Move beyond arbitrary percentage targets, such as “80% test coverage” because it sounds like a good number. Define what coverage actually means in your context.
Does every single endpoint need functional validation, or just the critical paths? Establish metrics that matter, such as test pass rate, defect escape rate, and pipeline execution time.
This is the hardest part of API testing.
APIs rely heavily on state. If your automated test requires an existing user ID to perform a PUT request, how does that ID get into the test database in the first place?
Decide how you will provision, sanitize, and tear down test data. Determine where you will use mock servers (service virtualization) to simulate unstable third-party APIs.
Choose tools that fit your team’s skillset. If your QA engineers are highly technical SDETs, code-based frameworks might work.
If you have manual testers or business analysts transitioning to automation, a low-code or no-code solution is vital for adoption. Ensure your chosen tools support your CI/CD platform natively.
Determine exactly when tests run. Lightweight smoke tests should run on every single pull request commit, whereas comprehensive integration suites might run nightly. Resource-heavy load tests might run weekly or right before major release candidates are cut.
Lightweight smoke tests should run on every single pull request commit, whereas comprehensive integration suites might run nightly.
Let’s look at a real-world application of how integrating this strategy streamlines enterprise delivery.
Experian Health’s heavy reliance on manual QA across complex data systems led to prolonged release cycles and created significant deployment bottlenecks for their core healthcare products.
They transitioned to an automated, model-based API and UI testing strategy using Tricentis Tosca, an AI-driven continuous testing platform, to seamlessly integrate validation into their CI/CD pipelines.
Experian Health achieved a 90%+ success rate on test execution, reduced full regression testing time from 1-2 weeks to just 20-30 minutes, and saved over 20,000 hours (nearly $1 million) in just six months.
Source: Experian Health case study
In life, execution matters just as much as planning. When you actually sit down to write the tests, adhering to best practices is what keeps your test suite from becoming a flaky nightmare a few months down the line.
Test A should never rely on the outcome of Test B. If tests must run in a specific sequence to pass, you will experience cascading failures that are impossible to debug when running in parallel.
Idempotency means a test can run 100 times and yield the exact same result without corrupting the database.
A 200 OK doesn’t mean the data is correct. You should also assert against specific JSON payload values, schema structures, and response times. Additionally, check the headers to ensure the right content type is being returned.
If your test creates a dummy user to test a GET endpoint, it should send a DELETE request at the end of the test block to wipe that user. Leaving junk data in your environments leads to test pollution, which causes bizarre failures when another test accidentally queries that orphaned data.
Stop hardcoding email addresses like testuser1@example.com into your scripts. By the second run, the API will likely reject it as a duplicate. You should try to generate dynamic, unique strings for your test payloads on every execution.
Leaving junk data in your environments leads to test pollution, which causes bizarre failures when another test accidentally queries that orphaned data.
Let me introduce some of the common challenges you may encounter:
Let’s imagine a scenario where Test A creates a user, Test B expects the database to be empty, and Test B will fail if they run in parallel.
You’ll need to design your tests to be highly independent and idempotent. If a test creates data, it should be responsible for tearing that data down via a DELETE request at the end of the run.
Better yet, spin up isolated, ephemeral databases via Docker for your CI/CD test runs so state is wiped clean every time.
Modern APIs use OAuth2, JWTs, or short-lived bearer tokens. Hardcoding tokens into your test scripts guarantees they will fail when the token expires in 60 minutes. Therefore, your API testing framework must be capable of chaining requests.
Step 1 of your test suite should dynamically request a fresh token from the authentication server, parse the token from the response payload, and pass it as a variable into the headers of all subsequent API calls.
A test that passes 80% of the time and fails 20% of the time without any code changes is worse than no test at all, since it destroys trust in the pipeline. Flakiness in API tests is almost always due to network timeouts, unresolved asynchronous background jobs, or database locks.
Implement robust retry logic in your tests, increase timeout thresholds for known slow endpoints, and ensure you are mocking third-party dependencies that are prone to latency.
An effective API testing strategy bridges the gap between fast-moving development teams and the business’s need for unshakeable reliability. It requires a shift in mindset by moving away from reactive bug-hunting towards proactive, contract-driven validation.
“Shifting left” means finding bugs when they are cheapest to fix. If an API returns the wrong data type for a critical field, catching that on a developer’s local machine costs a few minutes.
But catching it in production could cost thousands of dollars in downtime and emergency hotfixes.
By mapping tests directly into your CI/CD pipelines, you can build a safety net that actually empowers your developers to move faster, rather than treating QA as a final, cumbersome roadblock.
Today, agentic technology is being applied directly to API testing to solve the industry’s biggest headache, which is test creation and script maintenance.
Agentic AI is a form of artificial intelligence that can autonomously plan, execute, and adapt complex workflows to achieve a specific goal, rather than simply following a rigid script.
We are currently witnessing a massive shift in how AI is applied to software quality. In the past, AI in testing mostly meant smart assertions or visual regression algorithms on the frontend.
Today, agentic technology is being applied directly to API testing to solve the industry’s biggest headache, which is test creation and script maintenance.
Traditionally, if a developer updated an API contract, such as adding a new required field to a JSON payload, a QA engineer had to manually read the new Swagger documentation, find every test that hit that endpoint, update all the test payloads, fix the assertions, and push the new scripts. It’s exactly as it sounds: extremely tedious and low-value work.
Agentic AI changes this dynamic entirely. Instead of just executing a static script, an AI agent can ingest a specification and autonomously generate a comprehensive suite of functional, negative, and edge-case tests.
More importantly, when the API evolves, the agentic system can detect the schema change, understand the intent behind it, and self-heal the test suite by updating the payloads automatically.
You still define the overall strategy, but the agentic AI acts as a tireless junior engineer, handling the heavy lifting of script maintenance and test data generation.
This allows QA teams to focus on exploratory testing and complex integration scenarios rather than updating random tests on a weekday.
They say “Rome wasn’t built in a day,” and the same holds true for an effective API testing strategy. It requires assessing your current architecture, understanding your team’s limitations, and applying testing layers exactly where they will mitigate the most risk.
By defining your coverage goals, adopting risk-based prioritization, managing your test data intelligently, and leveraging modern agentic tools, you can transform API testing from a late-stage bottleneck into an automated enabler of velocity.
Ready to stop treating API testing as an afterthought? Discover how Tricentis Tosca can help your team scale automated, resilient API testing across your entire enterprise architecture.
This post was written by Deboshree Banerjee. Deboshree is a Senior Backend Engineer at Stripe and has previously held engineering roles at Goldman Sachs, Walmart, and tech lead roles at venture-backed startups. Throughout her career she has worked on large-scale distributed systems where data durability, redundancy, security, and operational reliability are critical concerns. Her experience evaluating enterprise software through the lens of scalability, resilience, and data protection informs her analysis of SaaS backup and recovery platforms.
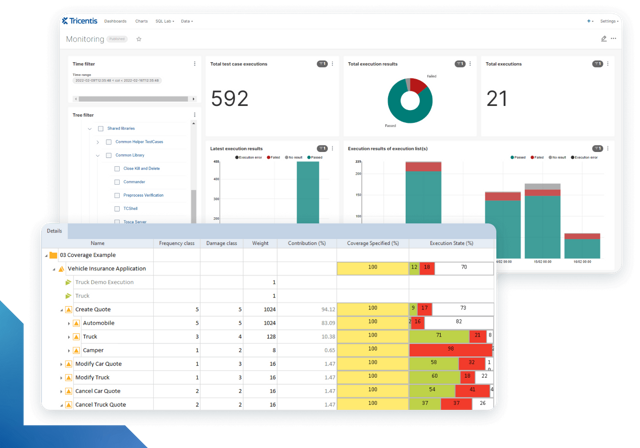
Learn more about intelligent test automation and how an AI-powered testing tool can optimize enterprise testing.
Learn more about intelligent test automation and how an AI-powered testing tool can optimize enterprise testing.
An API testing strategy is a comprehensive, documented plan outlining how an organization will validate its application programming interfaces.
It defines the tools, testing types, test data management processes, and CI/CD integration rules needed to ensure APIs are secure, functional, and performant before they reach production.
The core types include functional testing to verify business logic, contract testing to ensure data formats remain consistent, integration testing to check connections between internal services and databases, security testing to find vulnerabilities and authorization flaws, and load testing to evaluate system performance under stress.
Start by taking a complete inventory of all existing APIs and defining your coverage goals based on business risk.
Next, establish a framework for managing test data state and mock environments. Finally, select appropriate tools for your team’s technical skill level and map the automated execution of those tests into specific stages of your CI/CD pipeline.
Yes, API tests should run before UI tests in your deployment pipeline. Because API tests are headless, they are significantly faster, less brittle, and execute closer to the codebase.
They provide much quicker feedback to developers and can fail a bad build in seconds, long before time-consuming, resource-heavy UI tests are even triggered.